Welcome to my blog!

Meet the Author

Security is everyone's responsibility, fringilla nunc non, consectetur magna. Suspendisse potenti.

Looking for something?

Subscribe to this blog!

Receive the latest posts by email. Just enter your email below if you want to subscribe!

Friday, June 6, 2014

Windows 8 a 'threat' to China's security

Microsoft's Windows 8 has been branded a threat to China's cybersecurity in a state-backed news report.

https://ssl.bbc.co.uk/media/images/75320000/jpg/_75320136_021935474-1.jpg
China has worries about what happens to data stored on Windows 8 machines
China's CCTV broadcast a strongly critical story in which experts suggested it was being used to grab data about Chinese citizens.

The report comes only days after China banned the use of Windows 8 on many government computers.

Separately, other Chinese media firms called for tech firms that aided US spying to face "severe punishment".
US monitoring

In the story Prof Yang Min of Fudan University was quoted as saying that Windows 8 posed a "big challenge" to the nation's cybersecurity efforts,

"Microsoft would no longer open its Windows 8 source code to the Chinese government," he said. "However the security scheme of the Windows 8 operating system is designed to provide better access for Microsoft to users' database."

The report also suggested that Windows 8 was one of the methods the NSA was using to spirit data out of the country. China has been a consistent critic of the wide-ranging surveillance programme carried out by the NSA.

"Your identity, account, contact book, phone numbers, all this data can be put together for big data analysis," said Ni Guangnan, a member of the Chinese Academy of Engineering.

"The data might be a good way for the US to monitor other countries," he added.

In late May, China issued a notice which stopped Windows 8 machines being procured for government departments. The ban was apparently imposed because of a decree about energy-saving devices. However, many media reports said it was brought in because of fears over the security of the operating system.

Microsoft told CCTV that it was "actively co-operating" with the Chinese government on a review of its products to allay fears about what was being done with user data.

Many US tech companies were also criticised in the Chinese media for the help they have given to the NSA surveillance programme.

Yahoo, Cisco, Facebook, Apple, Google and others were described as "pawns" of the US government that had aided attempts to spy on Chinese citizens and steal secrets. All should be punished for their co-operation, said editorials in state-backed media.source

Bill to allow Tesla to sell cars in New Jersey advances.

A bill that would allow Tesla Motors Inc. to open four sales outlets selling the company’s electric cars in New Jersey gained approval from an assembly committee Thursday amid strong support from the environmental community.

http://www.northjersey.com/polopoly_fs/1.579240.1401981809!/fileImage/httpImage/image.jpg_gen/derivatives/box_650/0510b-telsa-50p-kk.jpg
The Tesla Model S rolling off an assembly line in June. The electric car was praised for performance and fuel efficiency.
The Assembly Consumer Affair Committee released the legislation - which allows the company to sells its vehicles directly to consumers, rather than through a dealership - after about an hour of almost of testimony that was entirely supportive.

The move comes about three months of the New Jersey Motor Vehicle Commission enacted a rule that required all new car vendors to sell their vehicles through a franchise, effectively shutting down two Tesla sales outlets - one in the Garden State Mall in Paramus and the other Short Hills. The two now operate as showrooms only, and can show but not sell cars.

Auto dealer groups argue that consumers are better served by franchise dealerships because they promote price competition and have more interest than dealers in responding to repair and recall issues. No dealers or industry representatives testified at the hearing.

Supporters of the measure said it should be passed because it would help control air pollution, create jobs and promote innovation.

“We can either embrace the fossil foolishness of the past” or pass the bill, said Jeff Tittle, executive director of the Sierra Club’s New Jersey Chapter. He said the measure would help the state tackle the fact that it has some of the worst air pollution in the nation.

Wireless computer of Intel will be the smart computer of 2016


https://upload.wikimedia.org/wikipedia/en/5/5b/Intel_i7_logo.png

Intel has been surprising people of this world since a long time. They are well known for their immense innovative ideas. Keeping that repute intact, they have come up with the idea of making Wireless computer this time. It is entirely a new concept in the world of technology.

This project is being done by the next generation platform of Intel called Skylake. They are expecting to launch this new form of Wireless computer by 2016 which will not require any cable for power or connections.

The senior VP of Intel who also turns out to be the general manager of PC client group explained this new technology at Taipei’s show. He said, “Charging, docking and display are few of those things which cannot be imagined without cables. But our new technology will be able to change this mainstream concept by eliminating cables.”

Cables have always been a matter of hassle and distress. Elimination of cable will take the technology of today’s world one step ahead. Intel has already made a sketch of how they are going to work and they have started their project too.

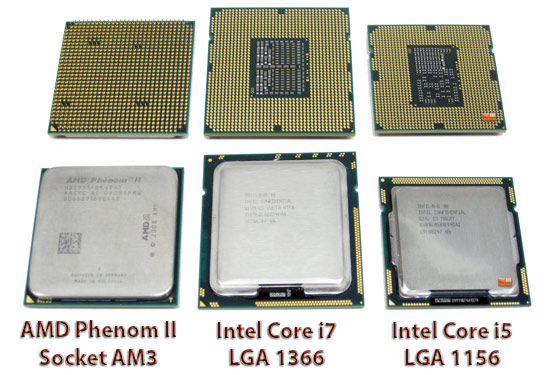
http://www.legitreviews.com/images/reviews/1060/intel_lynnfield_cpu.jpg
They will be using WiGig which is a new code of behavior for connectivity and docking. It transfers data at a speed of around 7 Gbps. WiGig connects to any laptop or tablet automatically as soon as it comes within the range, and disconnects as it moves away.

But most remarkable thing is getting power without using cables. Wireless computer will be using magnetic resonance for supplying power which can deliver power to more than one device. It can also pass power through a wood of thickness of 2 inches.

This form of delivering power has been demonstrated by charging headset, laptop, tablet and a cell at Computex by Skaugen. Wireless computer is going to be a huge success and will provide a new dimension to the computer world.


OpenSSL bug allows hackers to see private communication

The world hasn't yet recovered from the Heartbleed vulnerability in OpenSSL and now there's news of a new bug affecting the popular open-source security package. This recently announced, and already patched, exploit could allow an attacker to see and modify traffic between an OpenSSL client and an OpenSSL server.

https://s.aolcdn.com/dims-shared/dims3/GLOB/crop/3872x2546+0+0/resize/630x414!/format/jpg/quality/85/http://hss-prod.hss.aol.com/hss/storage/adam/7b8c7dc325713c36cb1a64484cc1314b/53294329.jpeg

This sounds worse than it really is. The extent of the issue is extremely limited because we're talking about specific versions of OpenSSL server. Plus, you need to be using that same server software on a client application, and the attack itself is quite a complicated affair.

The vulnerability, originally discovered in May by researcher Masashi Kikuchi, could allow for an attacker to lower the security of the communication between a client and a server using OpenSSL.

In fact, this point is key: the package has to be present on both ends and then the attacker has to use what's known as a "man-in-the-middle" attack, something not necessarily easy to do.

For the uninitiated, a man in the middle attack could be accomplished through a bit of compromised hardware -- like, say a router in your local coffee shop -- that strips the encryption from the information.

The bug affects all client versions of OpenSSL and servers on version 1.0.1 or 1.0.2-beta1, though it is recommended to update earlier versions as a precaution.

The biggest problem is that we don't really know how many of our applications are using this security package, as this information is not normally disclosed. That said, Adam Langley, a security engineer from Google, confirmed that desktop browsers such as "IE, Firefox, Chrome on Desktop and iOS, Safari, etc." are not vulnerable, as they don't use OpenSSL.


The problem is serious if all the required variables are in place, but you shouldn't worry about it too much. That is, if you're not a systems administrator. And you shouldn't even worry about using software with OpenSSL in general.

You may be surprised to hear this after the Heartbleed issue and this new problem, but the fact is that this latest exploit was discovered because there are more eyes reviewing the OpenSSL code, which means that the software is getting even better and safer.

Verizon demands Netflix stop messages on slow streaming


http://newsbcpcol.stb.s-msn.com/amnews/i/fc/5cf24d8b6bb83082248a15f372fa4c/_h0_w295_m6_otrue_lfalse.jpg

Verizon Communications Inc on Thursday demanded that Netflix Inc immediately stop displaying messages to customers that place blame on Verizon's broadband service for slow delivery of Netflix TV shows and movies.

The letter is the latest sign of tension between content providers like Netflix and Internet service providers over who should pay the price for companies that stream heavy traffic online.

In a cease-and-desist letter sent to Netflix, Verizon also asked the video streaming service to provide information including a list of customers on the Verizon network to whom Netflix delivered the notices, or face legal action.

"Failure to provide this information may lead us to pursue legal remedies," Verizon general counsel Randal Milch said in a letter to Netflix general counsel David Hyman.


In mid-May, Netflix started a test of messages displayed on the screen for some customers when a video is buffering. The messages say that there is congestion on the network of Verizon or another Internet service provider.

Netflix said on Thursday the test is continuing and meant to provide customers more information about their service, similar to a speed index that Netflix has published for months with a ranking of Internet service providers.

"This is about consumers not getting what they paid for from their broadband provider," Netflix spokesman Jonathan Friedland said. "We are trying to provide more transparency, just like we do with the ISP Speed Index, and Verizon is trying to shut down that discussion."

David Young, Verizon's vice president of federal regulatory affairs, told Reuters he felt the messages were part of a Netflix agenda to promote its views in Washington. Netflix has been urging the Federal Communications Commission to prevent broadband providers such as Verizon from charging Netflix fees for faster delivery of videos.

"That seems to be the motivation, to try to make a point or make points in that discussion that is going on in Washington D.C.,” Young said in a phone interview, though he wouldn't specify the issues.

In the letter, Verizon said the message's assertions were deceptive and inaccurate and that the responsibility for slow streaming on the site falls on Netflix.

Verizon said that in order to save money, Netflix relies on middlemen to distribute its content knowing that some of them have issues with congestion in some networks.

In April, Netflix said it reluctantly signed a deal to pay fees to Verizon to bypass those middlemen and deliver content directly to the company, ensuring faster speeds. But Verizon is still working to implement the needed architecture and expects to finish improvements by the end of 2014, said Young.

"I sincerely hope this is not a harbinger of things to come in terms of how Netflix treats its partners and our mutual customers," Milch said in the letter.

The Verizon notices came to light this week when a reporter who was a Verizon user tweeted about them. Comcast Corp, which also receives connection fees from Netflix, is not aware of any reports of Netflix buffering messages to its customers, a Comcast spokeswoman said.
Thursday, June 5, 2014

side share


side-share


==================

======================

==========================

<style type="text/css">
    #floating_bar {
    background-attachment:fixed;
    background:
        /* top, transparent White */
        linear-gradient(
        rgba(255, 255, 0, 0.2),
          rgba(255, 0, 255, 0.2)
        ),
        /* bottom, image */
        url(https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgvRj6dDS54KdFjPqsQH-_sOLcYYLRAweBhD9MF2Z0wkoxEvLZyehyodF1FxsXg4caw2PtI5dY2h2RmcpHAA_0Zk1HGGY3wghROU7h8c2RBuRDlQQ2aOt1iiCFrj1z5e63R3VndVGnMHUm5/s1600/bg.jpg);
    background-repeat: repeat;
    position:fixed;
    padding:0 0 3px 0;
    bottom: 30%;
    margin-left:-75px;
    float:left;
    border-top:2px groove #00a4ef !important;
    border-bottom:2px groove #ffb900 !important;
    border-right:2px groove #7fba00 !important;
    border-left:2px groove #f25022 !important;
    border-radius: 5px;
    -moz-border-radius:5px;
    -webkit-border-radius:5px;
    -webkit-box-shadow:1px 1px 1px rgba(0,0,0,0.2);
    box-shadow:1px 1px 1px rgba(0,0,0,0.2);
    z-index:10;
    }

    #floating_bar {
    clear:both;
    }
    </style>
    <div id='floating_bar'>
    <div style='margin:10px 0 5px 13px;' id='like'>
    <div class="fb-like" data-send="false" data-layout="box_count" data-width="40" data-show-faces="false"></div>
    </div>
    <div style='margin:0px 0 0 10px;' id='gplusone'>
    <g:plusone size="tall"></g:plusone>
    </div>

    <div style='margin:5px 5px 5px 6px;'>
    <a href="https://twitter.com/share" class="twitter-share-button" data-via="mybloggertriks" data-lang="en" data-count="vertical">Tweet</a>
    <script>!function(d,s,id){var js,fjs=d.getElementsByTagName(s)[0],p=/^http:/.test(d.location)?'http':'https';if(!d.getElementById(id)){js=d.createElement(s);js.id=id;js.src=p+'://platform.twitter.com/widgets.js';fjs.parentNode.insertBefore(js,fjs);}}(document, 'script', 'twitter-wjs');</script>
    </div>

    <div style='margin:5px 5px 5px 5px;' id='linkedin'>
    <script src="//platform.linkedin.com/in.js" type="text/javascript">
    lang: en_US
    </script>
    <script data-counter='top' type='IN/Share'></script>
    </div>
    <div style='margin:0px 0px 5px 10px;'>
    <a class="addthis_counter"></a>
    <script type="text/javascript" src="//s7.addthis.com/js/300/addthis_widget.js"></script>
    </div>
    <p style='line-height:10px; margin-bottom:8px; font-size:10px; font-weight:bold; text-align:center;'><a href='http://www.myblogger-tricks.com/2013/09/add-awesome-floating-sharing-bar-on.html' rel='nofollow' style='color:#777;'> Get Widget </a></p>
    </div>

=====================

==========================

Netflix blames slow speeds on Verizon, other Internet providers

Netflix Inc is telling customers that Verizon Inc and other Internet providers are to blame for slow speeds as the video streaming service pushes to avoid paying for faster delivery of its movies and TV shows.

http://newsbcpcol.stb.s-msn.com/amnews/i/ff/ec5efe65a3c7d2ea3b68e11dc2a/_h353_w628_m6_otrue_lfalse.jpg

Netflix has been calling on the U.S. Federal Communications Commission to do away with fees content companies pay to Internet service providers for smooth delivery of their services to consumers.

The FCC is expected to consider that idea as it seeks public comment on recently proposed Internet traffic, or "net neutrality," rules that suggest content companies should be allowed to strike "commercially reasonable" deals with broadband providers to give priority to their traffic.

"The Verizon network is crowded right now," reads a notice Netflix sent to some customers on the screen when a video is buffering.

Netflix is sending similar messages to U.S. customers of other broadband providers when the networks are congested, spokesman Jonathan Friedland said on Wednesday. The test began in mid-May and is reaching a few hundred thousand subscribers.

"We are testing ways to let consumers know how their Netflix experience is being affected by congestion on their broadband provider's network," he said. "At present, we are testing in the U.S. in areas serviced by many broadband providers."

Netflix for months has been telling customers around the world which Internet providers offer the fastest, or slowest, service through a speed index it posts on a company blog.

Verizon spokesman Robert Elek called the new alerts a "PR stunt."

"We're investigating this claim, but it seems misleading and could confuse people," Elek said.

In April, Netflix signed a deal to pay Verizon for faster delivery of its TV shows and movies. But the agreement has not taken full effect. Verizon is working to implement the needed architecture and expects improvements throughout 2014, a source with knowledge of the agreement said.

In a blog post on Wednesday, Verizon said Netflix chooses how to route its traffic. If speeds are slow, the company said, "the problem is most likely congestion on the connection that Netflix has chosen to use to reach Verizon’s network."

Netflix, which has raised concerns about the FCC's net neutrality proposal, has said it reluctantly agreed to pay Verizon and Comcast Corp for faster connections but believes the Internet companies should provide quicker delivery for free. Netflix Chief Executive Officer Reed Hastings argues free connections are key to ensuring "net neutrality," the equal treatment of data on the Internet.

Netflix may be trying to encourage customer complaints to regulators or broadband providers, BTIG analyst Rich Greenfield said.

"We suspect Netflix hopes (the buffering alerts) will generate enough call volume to ISPs, politicians and the FCC that it forces ISPs to rethink their paid interconnection policies," Greenfield said in a blog post.

U.S. technology companies beef up security to thwart mass spying

 A year after Edward Snowden exposed the National Security Agency's mass surveillance programs, the major U.S. technology companies suffering from the fallout are uniting to shore up their defenses against government intrusion.

http://newsbcpcol.stb.s-msn.com/amnews/i/9b/2055d69e3d38f4898c638dc48bbd9a/_h353_w628_m6_otrue_lfalse.jpg
Google on Wednesday said it was releasing a test version of a program allowing Gmail users to keep email encrypted until it reaches other Gmail users.
Instead of aggressively lobbying Washington for reform, Google Inc, Microsoft Corp and other tech companies have made security advancements their top priority, adopting tools that make blanket interception of Internet activity more difficult.

"It's of course important for companies to do the things under our own control, and what we have under our own control is our own technology practices," Microsoft General Counsel Brad Smith told Reuters. "I don't know that anyone believes that will be sufficient to allay everyone's concerns. There is a need for reform of government practices, but those will take longer."

As part of a "Reset the Net" campaign now reaching a mainstream audience, Google on Wednesday said it was releasing a test version of a program allowing Gmail users to keep email encrypted until it reaches other Gmail users, without the company decrypting it in transit to display advertising.

Google, Microsoft and Facebook Inc moved to encrypt internal traffic after revelations by Snowden, a former NSA contractor, that the spy agency hacked into their connections overseas. The companies have also smaller adjustments that together make sweeping collection more difficult.

"Anyone trying to perform mass surveillance is going to have a much harder job today than they would have even six months ago," said Nate Cardozo, a staff attorney with the civil liberties group Electronic Frontier Foundation.

Cardozo said the most-improved major company was Yahoo Inc, which went from not encrypting email by default to having protection comparable to that of its peers.

BUSINESS THREAT

The topic of boosting security has gained urgency after countries such as China faulted big tech companies as tools of a powerful U.S. surveillance state, and threatened to curb purchases of American tech products.

Surveillance opponents say the companies could do much more than they have. An NSA slide released last month by journalist Glenn Greenwald, titled "NSA Strategic Partnerships," touted "alliances with over 80 major global corporations" that supported the NSA's cyber offensive and defensive missions.

The slide named 12 companies, including the largest U.S. telecom carriers and Microsoft, Intel Corp, Hewlett-Packard Co and Cisco Systems Inc. None of those companies have renounced working with the agency or said that they would limit their cooperation to defensive measures.

All four of the tech companies in the group said they do not deliberately incorporate spying "back doors" into their products, but that leaves open a number of possibilities, including mandated or voluntary efforts to target individual customers or groups.

"Legally, the NSA can compel you to provide access to information," said Ashkan Soltani, a privacy researcher in Washington D.C. "The only way around this is to engineer systems to prevent access, or at least make it detectable." Google's new email tool is one example of that, and smaller companies are trying other formulas that retain little information about users.

PRESSING FOR REFORMS

The tech companies see improving their defenses as only the first step. Microsoft and other companies are also pressing governments to negotiate limits on cyber-spying.

A group of nine major companies formed a group called Reform Government Surveillance, which on Thursday took out newspaper advertisements urging the Senate to strengthen a House reform bill and ban bulk Internet surveillance.


Both Cisco and Microsoft also have said U.S. law should clearly protect data stored elsewhere. Smith said Microsoft would fight to overturn a recent federal magistrate's ruling forcing it to produce customer information from Dublin.

If that fails, Smith said, there are other means to draw the line at the U.S. border, including administration policy changes and new legislation.

Even if none of the three branches of government end up backing Microsoft's position, Smith said the company can change its business processes, such as by using joint ventures instead of subsidiaries, or its technology, such as by giving only users the encryption keys to their data.

Privacy Advocates Urge Senate to Rein In NSA Data Collection

On the same day that Google, Facebook and other tech companies urged stricter reforms to the National Security Agency’s surveillance policy, members of the Senate debated whether a bill passed by the House went too far or not far enough in protecting the privacy of Americans.

"The NSA has shown time and time again that it will seize on any wiggle room, and there is plenty of that in this bill," Sen. Tom Udall, D-N.M., said at a Senate Select Intelligence Committee hearing on Thursday.

Most of the debate centered on whether language modified by the House defeated one of the major goals announced by President Barack Obama in the spring: to limit the bulk collection of data by the National Security Agency.

The USA Freedom Act passed by the House left the "specific selection terms" — which define exactly what kind of information the NSA can request — too vague and broad for some people and too restrictive for others.

"There is nothing in this bill that would prohibit 'Verizon' or 'Gmail' or the state of Georgia from being used as a specific selection term," said Harley Geiger, senior counsel with the Center for Democracy & Technology, a privacy advocacy group.

Geiger and other privacy advocates want to limit those terms to specific people, phones or physical locations. White House officials, however, argued that strict definitions could limit law enforcement if they were searching for something without the benefit of specific names or telephone numbers, like all purchases of a chemical in a certain area.

Some of the speakers had some choice words for former NSA contractor Edward Snowden, who recently told "NBC Nightly News" anchor Brian Williams that he was trained as a spy and worked for the United States at high levels. Snowden kick-started the privacy debate by leaking thousands of classified documents last summer.

On Thursday, Georgia Sen. Saxby Chambliss referred to those leaks as "Snowden’s treasonous exposures."

"My phone data is in there with everybody else," said the Republican senator. "I’m not worried because I’m not talking to terrorists, and hopefully I’m not talking to anybody who is talking to terrorists."

Sen. Ron Wyden, D-Ore., Sen. John Rockefeller, D-W.Va., committee chairman Sen. Dianne Feinstein, D-Calif., and ranking member Sen. Saxby Chambliss, R-Ga., listen during a hearing before the Senate (Select) Intelligence Committee on Thursday.

Intel's gesture control promises hands-free life at Taiwan show

US computer chip giant Intel said its gesture-controlled technology could soon become part of everyday life as it showed its vision of a no-touch lifestyle in Taiwan Thursday.

http://newsbcpcol.stb.s-msn.com/amnews/i/6a/c15859979553c449d57d81532d51d4/_h353_w628_m6_otrue_lfalse.jpg
A woman operates a device with gesture-controlled technology during the Computex tech show in Taipei on June 4, 2014
Its stand at Computex, Asia's largest technology trade show, recreates a living space centred around a kitchen, illustrating how sticky fingers on screens and recipe books could be a thing of the past.

An actress with messy hands from cooking clicked through icons and apps and scrolled through cookery pages on a large monitor using just hand motions from around 12 inches (30 centimetres) away.

"This is a good example of the home usage of gesture," Intel's Jon Marshall told AFP, adding the technology harnesses voice recognition as well.

"We're trying to get a hands-free environment. Most people when they speak are animated -- it's a natural way to communicate. We're trying to take that to the next level in computing.

"It's going to mean more cameras, microphones -- the platform you're working with is going to natively recognise what you're doing."

The advances are the latest developments in Intel's sense technology which uses a camera with both 2-D and 3-D capabilities embedded into devices, enabling them to "see" depth and recognise facial expressions and movements.

Other companies that have rolled out gesture-control devices include Microsoft, which developed the Kinect accessory for its Xbox video game consoles which can recognise users, respond to spoken commands and detect a person's pulse.

Marshall, who is a senior technical marketing engineer at Intel, said the firm's gesture-controlled technology should be available on a range of devices by the end of the year.

Visitors at the show also tried their hand at controlling an old-fashioned fairground-style toy grabber game which uses the same hands-free technology, operating a metal claw through hand gestures detected by a camera.

As they closed their own hands into a claw shape, the metal grabber mimicked the motion.

"Traditionally you have to use keyboard or touches to activate your gadgets, now you may only need motions," said June Leung, programme director of the Chinese company TheBestSync which developed the grabber device.

"To me, this technology is a real breakthrough," Alexandre Straumann, product manager in IT hardware of France-based company Sources and Creation, said of the no-touch range.

"It could be applied everywhere and could really change our experience of living and entertainment."

Microsoft's top lawyer tells Uncle Sam to back off on surveillance

Microsoft's Brad Smith says the US government ought to end bulk collection of phone data, reform FISA court, and stop hacking data centers.

http://cnet3.cbsistatic.com/hub/i/2014/01/21/f2699b5f-8533-11e3-bc97-14feb5ca9861/97d25f134b206d7244cef9c8d045dcf4/76789484.jpg
Microsoft legal chief Brad Smith

Microsoft's top lawyer verbally gobsmacked the United States government on Wednesday, proposing a laundry list of surveillance reforms he says ought to get instituted immediately.

"It's now apparent that the government intercepted data in transit across the Internet and hacked links between company data centers," Brad Smith, Microsoft's general counsel, wrote in a blog post today. "These disclosures rightly have prompted a vigorous debate over the extent and scope of government surveillance, leading to some positive changes. But much more needs to be done."

Specifically,Smith urged the following:

   
Stop trying to force tech companies to turn over data in other countries, thus circumventing existing        treaties.
 
End the bulk collection of data of telephone records.
   
Reform the FISA court to make its proceedings more open.
 
Commit not to hack data centers or cables.
   
Do more to increase transparency.

Earlier in the year, President Obama issued a call for transparency as part of a general reform of NSA practices. Tech firms will now be able to disclose the total amount of FISA court orders they receive annually and the number of users affected by those requests, as long as they do so in bands of 250 or 1,000. But Smith's cri de coeur represents the growing frustration in the technology industry with the government's slow-footed response in the aftermath of the Edward Snowden revelations about the NSA's broad reach and intelligence-gathering practices.

"The US has both a responsibility and an opportunity to show new leadership on these issues," Smith wrote.

His decision to go public with his five-point complaint coincides with the one-year anniversary of the first leaked revelations about the extensive surveillance practices used by the National Security Agency to intercept phone and Internet records.

It's not the first time that Smith has gotten in Uncle Sam's face over surveillance. Earlier this year, he said in a blog that "government snooping potentially now constitutes an 'advanced persistent threat."

Massive dirt pile may have led to bridge closure


A contractor dumped a mountain of dirt about two stories high and 100 yards long next to an interstate bridge over several years, so much that it may have moved the ground and caused the bridge to tilt, state officials said Wednesday.

The Interstate 495 bridge, a major East Coast thoroughfare traveled by 90,000 vehicles daily, was closed Monday when engineers determined that bridge support columns were leaning.

The contractor said he was working with state officials to remove the dirt from the site, which he was allowed to use under an arrangement with a company that leases land. However, state officials said some of the dirt appeared to be on state land and a fence cordoning off the government's property was gone.

Officials aren't sure when the bridge will reopen to traffic, which has been detoured to Interstate 95. No major problems have been reported.


"I really feel bad about what happened," said contractor James Thomas Jr., 60. "I have absolutely no idea what happened, I really don't. ... I'm not a structural engineer. I'm not a bridge engineer."

Engineers suspect the weight of the dirt caused the ground underneath the bridge to shift. Four pairs of the bridge's support columns were tilting toward the pile of dirt.

Officials have said a system to shore up and brace the bridge will have to be designed, which will take weeks. State officials do not have an estimated price tag but have indicated that they might seek federal funds to help pay for the repairs.

Delaware Transportation Secretary Shailen Bhatt said officials did not know about the dirt mound until Monday, when engineers visited the bridge in response to a report received late last week. That report came from an engineer with a private company who was in the area on an unrelated project and saw cracking in the soil around the dirt pile. The engineer then spotted the leaning columns and contacted the transportation agency.

Thomas said he has worked in the area around the Port of Wilmington, just down the road from the bridge, for 41 years.

"I used to unload and load ships. I had a paving business and some other businesses. ... I've worn a lot of different hats down there," he said.

Thomas said no one had ever expressed concern about him storing dirt next to the bridge. He said he sells it as fill dirt.

Bhatt said: "I don't know where he gets his dirt or what he uses it for.... Our primary focus right now is just getting it out."

The DuPont Co. owns the land where the dirt is located and leases it out to a materials handing company called Port Contractors Inc.

Thomas's company, Keogh Contracting, has an arrangement with Port Contractors, which was founded by his father, to store dirt on the property.

Michael Evanko, president of Port Contractors, said his company is allowing Thomas to temporarily store dirt being removed from the bridge site on another parcel just down the road.

Built in 1974, the bridge is scheduled for inspection every two years and was last examined in October 2012.

Officials said they were examining aerial photographs in an effort to ascertain how long the dirt mound has been there.

"In 2012, there was some stuff out there but not very much; in 2013, a little more," Bhatt said. "Right now obviously there's a lot more dirt under there."

Crews plan to erect a new fence at the site after enough dirt is removed. Bhatt didn't know what happened to the original fence.

US general says SKorea databases hacked

The top U.S. military official in South Korea said a hacking incident might have compromised the personal information of thousands of South Koreans employed by the American command.


Gen. Curtis M. Scaparrotti, commander of U.S. Forces in South Korea, apologized Thursday for the "possible theft" from two databases of private details of South Koreans such as names, contact information and work history.

About 16,000 current and former workers, almost all of them Korean nationals, and people who have sought jobs with the U.S. military in South Korea, are affected by the incident.

The U.S. military said no classified military data was compromised as the databases were on a separate network.

South Korean government, broadcasting and finance industry networks have been a frequent target of cyberattacks in the past. Some have been blamed on North Korea, which denies any involvement. Others have been attributed to hackers seeking to profit from data theft.

U.S. Forces spokesman Christopher Bush said an investigation by the U.S. Army was underway to determine who was responsible.

The U.S. has around 28,500 soldiers in South Korea as a deterrent against the North. The 1950-1953 Korean War ended in a truce so the peninsula is still technically at war.

Softbank enters robotics with emotional humanoid

Softbank Corp. is entering the robotics business with its cooing, gesturing and sympathetic Pepper humanoid-on-wheels that it says is designed for companionship and can decipher human emotions.


The Japanese mobile carrier said Thursday that Pepper will go on sale in Japan in February for 198,000 yen ($1,900). Overseas sales plans are under consideration but undecided.

The machine, which has no legs, but has gently gesticulating hands appeared on a stage in a Tokyo suburb, cooing and humming. It dramatically touched hands with Softbank Chief Executive Masayoshi Son in a Genesis or "E.T." moment.

Son, who told the crowd that his longtime dream was to go into the personal robot business, said Pepper has been programmed to read the emotions of people around it by recognizing expressions and voice tones.

"Our aim is to develop affectionate robots that can make people smile," he said.

Cuddly robots are not new in Japan, a nation dominated by "kawaii," or cute culture, but no companion robot has emerged a major market success yet.

Japanese electronics and entertainment company Sony Corp. discontinued the Aibo pet-dog robot in 2006, despite any outcry from its fans. At that time, Sony had developed a child-shaped entertainment robot similar to Pepper but much smaller, capable of dances and other charming moves, which never became a commercial product.

Honda Motor Co. has developed the walking, talking Asimo robot, but that is too sophisticated and expensive for home use, and appears in Honda showrooms and gala events only. Even then, it is prone to glitches because of its complexity.

Many other Japanese companies, including Hitachi Ltd. and Toyota Motor Corp., not to mention universities and startups, have developed various robots, big and small, that entertain and serve as companions.

There is little emphasis on delivering on practical work, in contrast to industrial robots at factories and military robots for war.

But the potential is great for intelligent machines as the number of elderly requiring care is expected to soar in rapidly-aging Japan in coming years. Robotics are already used to check on the elderly and monitor their health and safety, but they might also play a role in reducing feelings of loneliness and isolation.

The 121 centimeter (48 inch) tall, 28 kilogram (62 pound) white Pepper, which has no hair but two large doll-like eyes and a flat-panel display stuck on its chest, was developed jointly with Aldebaran Robotics, which designs, produces and sells autonomous humanoid robots.

Besides featuring the latest voice recognition, Pepper is loaded with more than a dozen sensors, including two touch sensors in its hands, three touch sensors on its head, and six laser sensors and three bumper sensors in its base.

It also has two cameras and four microphones on its head and has Wi-Fi and Ethernet networking capabilities.

In Thursday's demonstration, Pepper sang, "I want to be loved."

Softbank said Pepper can dance and tell jokes. The machine will be on display starting Friday at Softbank retailers, the company said.

Softbank, which now owns Sprint of the U.S. and boasts more than 100 million subscribers globally, has been growing rapidly as a mobile carrier in Japan, boosted by being the first to offer Apple's iPhone.

Pepper was jointly developed with Aldebaran Robotics, which has offices in France, China, Japan and the U.S. and is 78.5 percent owned by Softbank.

"I've believed that the most important role of robots will be as kind and emotional companions to enhance our daily lives, to bring happiness, constantly surprise us and make people grow," said Bruno Maisonnier, founder and chief executive of Aldebaran, who appeared on the stage with Son.

Aldebaran has produced more than 5,000 of its Nao humanoid, its first product, which is used for research and educational purposes.

Pepper can get information from cloud-based databases and comes with safety features to avoid crashes and falls, and its capabilities can grow by installing more robot applications, according to Softbank.


U.S. companies seek cyber experts for top jobs,board seats

Some of the largest U.S. companies are looking to hire cybersecurity experts in newly elevated positions and bring technologists on to their boards, a sign that corporate America is increasingly worried about hacking threats.

http://newsbcpcol.stb.s-msn.com/amnews/i/82/c88e34d86efa2406c4bc198f26fc1/_h353_w628_m6_otrue_lfalse.jpg
An illustration picture shows projection of binary code on man holding aptop computer in Warsaw
JPMorgan Chase & Co, PepsiCo Inc, Cardinal Health Inc, Deere & Co and The United Services Automobile Association (USAA) are among the Fortune 500 companies seeking chief information security officers (CISOs) and other security personnel to shore up their cyber defenses, according to people with knowledge of the matter.

While a CISO typically reports to a company's chief information officer (CIO), some of the hiring discussions now involve giving them a direct line to the chief executive and the board, consultants and executives said.

After high-profile data breaches such as last year's attack on U.S. retailer Target Corp, there is now an expectation that CISOs understand not just technology but also a company's business and risk management.

    "The trend that we are seeing is that organizations are elevating the position of the CISO to be a peer of the CIO and having equal voice associated with resource priorities and risk decisions," said Barry Hensley, executive director at Dell SecureWorks' Counter Threat Unit.

    With many companies looking for security executives with military or defense backgrounds, people with the right expertise can command increasingly higher salaries.

Large corporations have recently hired CISOs for between $500,000 and $700,000 a year, according to Matt Comyns, global co-head of the cybersecurity practice at search firm Russell Reynolds Associates. Compensation for CISOs at some technology companies with generous equity grants have reached as high as $2 million, he said.

In comparison, CISOs who have been with a company for five or more years are on $200,000 to $300,000 per year, Comyns said.

NEW URGENCY

Security experts have often criticized corporate America for being too complacent about cyber risks and for not doing enough to protect their computer networks from hackers.

A recent PwC survey found the vast majority of cybersecurity programs fell far short of guidelines drafted by the Commerce Department's National Institute of Standards and Technology (NIST). Only 28 percent of more than 500 executives surveyed said their company had a CISO or Chief Security Officer.

But high-profile data breaches, such as the one at Target, have injected a new sense of urgency, executives said. Target ousted its CEO, Gregg Steinhafel, earlier this month, and its chief information officer, Beth Jacobs, resigned in February. The retailer is now searching for a CISO, a newly created role.

    "This is ringing bells at the C-suite," Charlie Croom, vice president of cybersecurity solutions at U.S. defense contractor Lockheed Martin Corp told the Reuters Cybersecurity Summit.

Recruiters and executives said companies are increasing both the size and budget of their security teams. By the end of 2014, JPMorgan's annual cybersecurity budget will rise to $250 million from $200 million in 2012, CEO Jamie Dimon said in April. And the largest U.S. bank will have about 1,000 people focused on cybersecurity, compared with 600 people two years ago, he said.

A JPMorgan spokesman said the bank will continue to invest and expand its security team, but declined to confirm if the firm was looking for a CISO.

Cardinal Health CIO Patty Morrison said the healthcare services company was looking to hire a vice president of security to bring in "new talent and new ideas." USAA Chief Security Officer Gary McAlum confirmed the diversified financial services group was looking for a CISO.

Deere representatives were not available for comment, while a spokesman for PepsiCo declined to comment. The soft drink and snack maker lost its CISO, Zulfi Ahmed, to MetLife Inc earlier this year.

CHANGING FACE OF BOARDS

As companies look for CISOs, many boards are seeking directors with technology know-how so that they can better understand cyber risks. Matt Aiello, co-head of the cyber practice at Heidrick & Struggles, said he is seeing "unprecedented" demand for CIOs to serve on boards.

"Boards don't feel they have the right expertise to draw upon. It is not that they don't understand it is a risk; they don't want to blunder uninformed into it," said David DiBari, managing partner at the law firm Clifford Chance in Washington.

Retired Accenture CIO Frank Modruson, former Department of Defense CIO Teresa Takai, Dell SecureWorks chief Mike Cote and AT&T Inc CISO Ed Amoroso have all been approached to serve as potential directors, according to people with knowledge of the situation.

Takai said she is "looking at a couple of things," including with a security technology company. Cote, through a Dell spokeswoman, confirmed he has been approached by several companies about serving on their boards. An AT&T spokesman declined to comment on behalf of Amoroso. Modruson was not available for comment.

Pamela Craig, who serves on the boards of Akamai Technologies Inc, Wal-Mart Stores Inc and software maker VMWare Inc, expects demand for CIOs to serve on public boards to increase. "You need people who have direct first-hand experience in the boardroom," she said.

Some boards are also considering moving responsibility for network security to risk committees from audit committees, as cybersecurity is increasingly viewed as a business risk more than a compliance issue, according to Mary Galligan, director of Cyber Risk Services at Deloitte & Touche LLP.

RSA Security Senior Vice President Amit Yoran said boards are looking for experts who can help them build security into products in development, rather than bolting it on at the last minute.

"CISOs are being brought to the business table more often," Yoran said. "This is a realization that in many cases a business's survival relies on the security of the technology."
Wednesday, June 4, 2014

Cloud Turbulence: Feature Creep Means New Clashes in the Cloud Market

As cloud services mature and add features, they increasingly overlap, signaling heightened competition in both the consumer and enterprise markets.

Smaller cloud players must be nimble and adaptive to avoid getting trampled.

http://blogs-images.forbes.com/kurtmarko/files/2014/06/Supercell-Panoromas-Texas.jpg

The cloud is the latest battleground of the tech titans across the spectrum of enterprise and consumer business, but maturation, a desire for market hegemony and technology evolution naturally lead to new features and that means formerly disparate services are encroaching upon one another. The last week has provided two great examples. First, Amazon released the AWS Management Portal for vCenter, a plugin for VMware’s omnipresent, at least in the enterprise where where surveys routinely show the company’s penetration north of 60%, vCenter management software, vCenter management software that allows migrating VMs to EC2 and managing them alongside private cloud vSphere resources. If it wasn’t clear from the product title, this quote makes clear Amazon is taking a shot squarely aimed at VMware’s core business and nascent vCloud Hybrid Service (VCHS) (italics added):

    If you have invested in learning VMware and have trained on virtualization tools like vCenter, the portal lets you leverage your experience, while benefiting from the infrastructure, APIs, tools, and ecosystem that AWS provides. As you gain experience with AWS, you can use the portal in combination with other AWS tools, like the AWS Management Console and the AWS CLI, or even migrate to using those tools in place of the portal if you decide that it no longer meets your needs or if you move off of using VMware is the future.

VMware’s response, in the form of a lengthy blog post by CTO Chris Wolf demonstrates that the company both recognizes the threat and takes it seriously. After some introductory fluff about the benefits of hybrid cloud strategies and a unified management platform, Wolf gets to the point by offering a litany of shortcomings in Amazon’s product: it’s hard to move workloads back and forth, you can’t use existing software licenses, it doesn’t provide software automation for both private and public clouds, it doesn’t enforce enterprise security and policy across clouds and it doesn’t work with other third-party VMware plugins. Wolf’s closing argument is clearly directed at enterprise CIOs and IT pros, not the developers, startups and new tech businesses that are Amazon’s bread and butter:

    Whether you are strategically aligned to VMware or not, you should demand consistent management, third party integration, and a common API that spans all hybrid cloud deployment scenarios. Don’t be fooled by basic management that is tactically useful today but can lead to increased lock-in down the road. The cloud service broker has to be multi-provider -– vCloud Automation Center is today and has been for some time. Beyond that – the hybrid cloud platform should enable provider choice and seamless third party integration, regardless of where a workload is deployed. Deciding to run a workload somewhere else should not require a massive migration effort along with massive costs.

In sum, as The Register aptly points out, Amazon is offering a Trojan Horse designed to wean users from the friendly confines of VMware’s ecosystem. Like all Trojan’s, it’s a gift with unintended consequences that once in the front gate can make life very difficult for IT and mean later switching public cloud providers exceedingly complicated. Amazon is betting that its market dominance, rich feature set and a convenient, familiar administrative interface will be enough to win devoted VMware customers. VMware is counting on strategic-thinking IT execs to consider the long term implications of embracing an alternative cloud.

All’s not quiet on the consumer front as Apple AAPL +1.14% retools iCloud

There’s an equally compelling battle brewing among consumer cloud services that got much more interesting this week as Apple unveiled a series of enhancements to its core operating systems and iCloud platform at its Worldwide Developer’s Conference. By adding iCloud Drive, CloudKit and app extensions Apple addresses long-standing complaints about its incomplete cloud services and mobile operating system.

With Drive, iCloud becomes a full fledged cloud filesystem accessible from iOS, Mac OS X or Windows (but unsurprisingly, not from Android), just like Dropbox, Box, and Google Drive. By simultaneously announcing significant price cuts, down to 99 cents per month for 20GB and $3.99 for 200GB, Apple essentially matches Google (which charges $1.99 per month for 100GB) and significantly undercuts Dropbox.

iCloud will also be much cheaper than Box, but there are a couple reasons its CEO Aaron Levie is anything but worried. First, Box is moving up the food chain from being a provider of raw storage to that of an enterprise content management and collaboration platform. Indeed, it’s IPO S–1 filing spells out the strategy:

    Box provides a cloud-based, mobile-optimized Enterprise Content Collaboration platform that enables organizations of all sizes to easily and securely manage their content and collaborate internally and externally.

The other reason Levie is sanguine about the developments at WWDC are app extensions, namely new iOS APIs that provide Android-like flexibility in how apps share data. No longer will iOS apps be locked into iCloud, reliant on a cloud service like Dropbox to develop an independent set of storage APIs or forced engineer their own. Instead, iOS storage provider extensions will allow easy integration for any cloud service. As Levie said at WWDC, Extensions eliminate the “virtual moats” around mobile app data. “This,” he said, “is going to be really powerful set of capabilities. And it’s going to give Apple a massive advantage.” Levie’s optimism may be premature since Apple’s advantage may not devolve to Box. It will be equally simple for all of its enterprise competitors like EMC Syncplicity, Egnyte, Citrix ShareFile or even Microsoft to build iCloud hooks into their own services.

Collision of cloud backends

CloudKit was Apple’s other major cloud announcement and here too we see evidence of encroachment into other cloud services. Designed to make it much easier for app developers to use iCloud as a storage and database backend, CloudKit sounds quite similar to other backend infrastructure and backend as a service (BaaS) products like Google’s Mobile Backend Starter, Azure, AWS, Parse and Kii. Of course Apple is focused on enabling its own developers, not providing a general purpose platform for Android or Windows, but CloudKit is just another example of how the narrow silos around targeted cloud services are crumbling.


Cloud services are the latest realm in the technology industry’s quest to build compelling, defensible and sticky ecosystems. As such, the dominant tech giants will continue to expand their reach and further intrude on each other’s turf in both the enterprise and consumer markets. The jostling will create plenty of news and be fun to watch, but smaller cloud players must be nimble and adaptive to avoid getting trampled.source

Google Gets 10,000 Requests -A Day- To Be ‘Forgotten’ in Europe

Individuals in Europe hoping to have search results deleted have sent Google an average of 10,000 requests per day, or one every 7 seconds.

http://newsbcpcol.stb.s-msn.com/amnews/i/ef/7dfa528c7d973e46640ac5ca9436/_h353_w628_m6_otrue_lfalse.jpg
Google is starting to accept requests from Europeans who want to erase unflattering information from the results produced by the world's dominant search engine. The demands can be submitted on a Web page that Google opened late Thursday, May 29, 2014, in response to a landmark ruling issued two weeks ago by Europe's highest court.
Google is receiving a deluge of requests from people hoping to delete individual search results, as Europeans exercise their newly-won “right to be forgotten.”

Google said Tuesday it had received 41,000 requests from people in the first four days after posting a request page late last week, the Wall Street Journal reports, amounting to more than 10,000 requests per day, or roughly 7 each minute.

The Luxembourg-based European Court of Justice ruled last month that search engines must accept requests to remove links from individual name searches. Critics of the court’s ruling say it could limit free speech and allow for a whitewashing of the internet.

The sheer volume of requests has led Google to consider hire new staffers or re-dedicating staffers to deal with submissions.

Turkey lifts block on access to YouTube: official

Turkey's telecoms regulator removed an official order blocking access to YouTube <GOOGL.O> from its website on Tuesday after the country's top court ruled last week that the ban was a breach of human rights.

http://newsbcpcol.stb.s-msn.com/amnews/i/af/a7af5d3d74309eaae4f9fcc223c0/_h353_w628_m6_otrue_lfalse.jpg
YouTube logos displayed on a laptop screen partially covered with Turkey's national flag in this photo illustration taken in Ankara.
The video-sharing website will be accessible in Turkey later on Tuesday, an official at Prime Minister Tayyip Erdogan's office told Reuters. "As the Constitutional Court verdict was received today, YouTube will be open to access later today."

Blocks on access to YouTube and Twitter <TWTR.N> were imposed after illicit audio recordings, purportedly revealing corruption in Erdogan's inner circle, were leaked on the sites. The block on access to Twitter was lifted in April.

The ban on YouTube was imposed on March 27 in the build-up to local elections after a tape of top security officials discussing possible military intervention in Syria was leaked.

Erdogan condemned the tape recording, which followed a series of other leaked wiretaps, as an act of treason. He subsequently emerged from local elections on March 30 with his popularity largely intact.

Turkey's highest court, deliberating appeals submitted by individuals challenging the ban, last week ruled that the block was a violation of the right to freedom of speech.

U.S. leads global effort to disrupt cyber crime ring

A U.S.-led international operation disrupted a crime ring that had infected hundreds of thousands of PCs around the globe with malicious software used for stealing banking credentials and cyber extortion, the Justice Department said on Monday.

Authorities used technical and legal tactics to interrupt the so-called botnet's operations, shutting down the servers the cyber criminals used to control infected machines and causing those machines to "phone home" to servers controlled by law enforcement.

"These schemes were highly sophisticated and immensely lucrative, and the cyber criminals did not make them easy to reach or disrupt," Leslie Caldwell, who heads the Justice Department's criminal division, told a news conference.

The botnet, known as Gameover Zeus, or GOZ, derives its name from a version of the Zeus credential-stealing software, which U.S. court documents said have caused $100 million in losses to consumers and businesses since it first surfaced in 2007. Court documents released on Monday said that between 500,000 and 1 million machines worldwide were infected with the malicious software, or malware.

Its primary purpose was to capture banking credentials, though it has been known to change recipients of legitimate payments orders, for example targeting U.S. hospitals' payroll operations.

A botnet is a group of computers under the control of someone other than the computers' owners. They are typically assembled through viruses and are the key tool in spam, online bank fraud and denial-of-service attacks on websites.

GOZ was also used to distribute Cryptolocker, malicious software known as "ransomware" that encrypts data of an infected computer, making it inaccessible to the user. Cyber criminals would essentially take the machine hostage, promising to unscramble the data if the user paid them a ransom of as much as $700, the Justice Department said.

The U.S. Department of Homeland Security set up a website to help victims remove the GOZ malware: https://www.us-cert.gov/gameoverzeus .

The European Cybercrime Center also participated in the operation, along with Australia, Canada, France, Germany, Italy, Japan, Luxembourg, New Zealand, Ukraine and the United Kingdom.

Intel Corp, Microsoft Corp, security software companies F-secure, Symantec Corp, and Trend Micro ; and Carnegie Mellon University also supported the operation.

The U.S. government kept the effort secret until Monday when it unsealed a 14-count indictment accusing Russian national Evgeniy Mikhaylovich Bogachev of involvement in the alleged conspiracy.

The suspect, who authorities said is known online as Lucky12345, is charged with writing computer code used to compromise banking systems and assist others in stealing banking credentials, according to court documents.

Prosecutors said the victims of the attacks included Capital One Bank, Bank of Georgetown in Washington, and First National Bank of Omaha.

Bogachev and his group infected thousands of business computers with software that captured passwords, account numbers, and other information used to log in to online bank accounts, prosecutors said. (Additional reporting by Alina Selyukh; Editing by Jonathan Oatis)

China state media calls for 'severe punishment' for Google, Apple, U.S. tech firms

Chinese state media lashed out at Google Inc, Apple Inc and other U.S. technology companies on Wednesday, calling on Beijing "to punish severely the pawns" of the U.S. government for monitoring China and stealing secrets.

http://newsbcpcol.stb.s-msn.com/amnews/i/ef/83bb65b7852cce06c638949a44c1/_h353_w628_m6_otrue_lfalse.jpg
A person poses with a magnifying glass in front of a Google search page in this illustrative photograph taken in Shanghai.
U.S. companies such as Yahoo Inc, Cisco Systems Inc, Microsoft Corp and Facebook Inc threaten the cyber-security of China and its Internet users, said the People's Daily on its microblog, in comments echoed on the front page of the English-language China Daily.

It is not clear what sparked this latest round of vitriol, nor what information the U.S. firms are alleged to have stolen. But Chinese media have repeatedly attacked American tech companies for aiding the U.S. government's cyber espionage since U.S. National Security Agency (NSA) contractor Edward Snowden revealed widespread spying programs including PRISM.

Under PRISM, the NSA seized data from companies such as Google and Apple, according to revelations made by Snowden a year ago.

Chinese state-owned firms have since begun dispensing with the services of U.S. companies such as IBM Corp, Oracle Corp and Cisco in flavor of domestic technology. As a result, Snowden's revelations may cost U.S. companies billions of dollars, analysts say.

"U.S. companies including Apple, Microsoft, Google, Facebook, etc. are all coordinating with the PRISM program to monitor China," the People's Daily said on its official microblog.

"To resist the naked Internet hegemony, we will draw up international regulations, and strengthen technology safeguards, but we will also severely punish the pawns of the villain. The priority is strengthening penalties and punishments, and for anyone who steals our information, even though they are far away, we shall punish them!" it said.

Google has already had problems in China this week. On Monday, a China censorship watchdog said Google services were being disrupted ahead of Wednesday's 25th anniversary of the 1989 crackdown on pro-democracy demonstrators around Beijing's Tiananmen Square.

"We cannot say this more clearly - the (U.S.) government does not have access to Google servers - not directly, or via a back door, or a so-called drop box," said Google Chief Legal Officer David Drummond in an emailed statement on Wednesday. "We provide user data to governments only in accordance with the law."

Microsoft declined to provide immediate comment. Facebook, Yahoo, Apple and Cisco were not immediately available when Reuters sought comment by telephone and email.

Facebook is currently blocked by Chinese censors, but said last month it may open a sales office in China to provide more support to local advertisers who use the website to reach customers overseas.

ROCKY TIME

In December, Google, Microsoft, Apple, Facebook, Yahoo and other Internet companies issued an open letter to U.S. President Barack Obama and Congress to reform and introduce restrictions on surveillance activities.

Even so, U.S. tech companies have had a rocky time in China since the NSA revelations. Just last month, central government offices were banned from installing Windows 8, Microsoft's latest operating system, on new computers.

But the U.S. has responded with its own measures. In May, the U.S. Department of Justice charged five Chinese military officers with hacking U.S. companies to steal trade secrets.

The indictment sparked outrage in China and added urgency to Beijing's efforts to promote the development of local information technology (IT) companies.

Chinese media called the United States "a high-level hooligan" and officials accused Washington of applying "double standards" on issues of cyber spying.

After the charges were announced, China said it will investigate providers of important IT products and services to protect "national security" and "economic and social development."
 
© Copyright 2010-2014 Tutorneto All Rights Reserved.
Edit by Edit | Edit by Edit | Edit by Edit.